HOW DO YOU CREATE ROLE-BASED SALES COLLATERAL LIBRARIES?
SEPTEMBER 30, 2026



SDR
Outreach templates, one-pagers, competitive one-liners
AE
Full deal collateral: decks, case studies, pricing, proposals
Sales Manager
Everything AEs see, plus coaching and onboarding material
Partner / Reseller
Co-branded and partner-approved assets only
Customer Success
Onboarding guides, renewal decks, expansion content
Admin
Full library, including drafts and archived versions
A rep on your team just sent a prospect a pricing sheet that expired two quarters ago. Somewhere in a shared drive, a partner downloaded an internal-only battlecard meant for your own AEs. Nobody did anything malicious here. They just had access to everything, and "everything" is exactly the problem role-based sales collateral libraries exist to solve.
Instead of one shared folder where anyone can grab anything, a role-based library ties access to a role, AE, SDR, partner, customer success, admin, so each person sees a version of the library built for what they actually do. If you haven't tackled the tagging and structure side of this yet, organizing sales collateral effectively is the companion piece to read first. This guide walks through what a role-based setup looks like on top of that, why flat access breaks down as a team grows, and the five steps to build one from scratch.
What Is a Role-Based Sales Collateral Library?
A role-based sales collateral library is a content library where access is granted by job function or team instead of by individual user. Reps, managers, and partners each see only the content assigned to their role, so nobody has to sort approved material from things that were never meant for them.
That single distinction changes how the library behaves as headcount grows. A flat library treats every person the same and relies on someone remembering to police it. A role-based one treats every role the same, and a person just inherits whatever that role is entitled to see.
Role-Based vs. Individual Content Permissions
Individual permissions are set person by person: someone in ops opens the tool, finds the new hire, and manually grants access to a folder here and a collection there. It works for ten people. By fifty, it's a part-time job, and by two hundred, nobody's confident the permissions still match reality.
Role-based access control flips the sequence. You define the role once (what an SDR sees, what a partner sees, what a sales manager sees), and every person assigned that role inherits the same access automatically. A new hire in an existing role needs zero manual setup. A departing employee's access disappears the moment their role is removed, not whenever someone remembers to clean up their folder permissions.
Why Role-Based Access Matters for Sales Teams
Sales enablement content management isn't really a storage problem. It's a trust problem wearing a storage problem's clothes.
When everyone can see everything, three things tend to happen at once: outdated collateral stays in circulation because nobody owns removing it, reps waste time filtering through content that was never theirs to use, and sensitive material (unreleased pricing, internal competitive notes, pre-launch decks) sits one careless share away from a prospect's inbox. None of that requires bad intent. It just requires a library with no structure telling people where the edges are.
The Cost of Flat, No-Permission Libraries
A Content Hub view scoped to a single role, versus the same hub with no permissions applied.
Picture the same content hub two ways. In the flat version, a new SDR opens the library to 40 folders, half of them named things like "OLD - do not use" or "Draft - legal review pending," and has no way to tell which is which. In the role-scoped version, that same SDR opens the hub to exactly what an SDR needs: outreach templates, one-pagers, competitive one-liners. Nothing else is visible, so there's nothing to get wrong.
Group-based permissions are what make the second version possible without someone manually curating every person's view.
How to Create a Role-Based Sales Collateral Library
You set up role-based access by defining your roles first, structuring the content hub's categories around them, assigning permissions to each role as a group, packaging role-specific collections on top of that structure, and making sure search results stay scoped to what each role can already see.
The order matters. Skip straight to permissions before you've mapped the roles, and you'll spend the next year re-configuring access every time someone's title changes.
Step 1: Map Your Roles and Buyer-Facing Personas
Setting up a user group tied to a specific role inside the content platform.
Start with the roles that actually exist in your go-to-market motion, not a generic template. Most teams land somewhere around six: AE, SDR, sales manager, partner or reseller, customer success, and admin. Resist the urge to create a role for every job title. A role only earns its own permission set if it genuinely needs a different slice of content than the roles around it.
Step 2: Structure Your Content Hub Around Those Roles
Category and folder architecture inside a content hub, organized to mirror the roles that use it.
A content hub that's organized by file type (all decks here, all one-pagers there) forces every role to dig through the same undifferentiated pile. Organize it by who uses the content instead: a category for AE deal support, one for partner-facing material, one for CS. File type becomes a filter inside each category, not the primary structure.
Step 3: Set Group-Based Permissions, Not Individual Ones
Assigning view and edit permissions to a role group rather than to individual users.
This is the step that actually enforces everything you've mapped so far. Assign permissions to the role group, not to each person inside it. When someone joins the AE team, they get the AE role and inherit AE-level access instantly. When someone changes teams, you swap their role instead of manually revoking a dozen individual grants and hoping you didn't miss one.
Step 4: Build Role-Specific Collections and Sales Kits
A curated sales kit collection scoped to a specific role, ready to hand to a new hire.
Once the structure and permissions exist, package them. A "New AE Kit" collection, a "Partner Enablement Kit," a "Q3 Renewal Playbook" for CS, these are curated bundles that sit on top of your role-based access, not a replacement for it. Content hub tools that support collections let you build these once and keep them current without rebuilding the bundle every time a new asset gets approved.
Step 5: Make Content Findable Within Each Role's View
Search results filtered by persona and buyer stage, staying within the boundaries of what the searching role can access.
Permissions solve who can see what. Search has to respect that same boundary, or you've built a locked door with a window right next to it. When an AE searches "renewal deck," results should only surface what an AE is permitted to see, filtered further by persona and deal stage if your library supports that layer. Get this wrong and a well-meaning search feature quietly undoes every permission you just set.
Common Mistakes When Setting Up Role-Based Access
Over-segmenting is the most common failure. Teams create fifteen roles to capture every nuance of the org chart, and now reps in adjacent roles can't share content that should obviously be shared between them. Start with the six roles above and only split further when two people in the same role genuinely need different access.
The second mistake is setting permissions once and never auditing them. Roles drift: a partner tier gets renegotiated, a team reorganizes, a product line gets sunset, and the permission structure quietly stops matching reality. A quarterly review catches this before it becomes a compliance problem instead of a housekeeping one.
The third is confusing "role" with "individual." If you find yourself granting one-off exceptions to specific people inside a role, that's usually a sign you need a new role, not a growing list of exceptions bolted onto an old one.
How Paperflite Handles Role-Based Content Hub
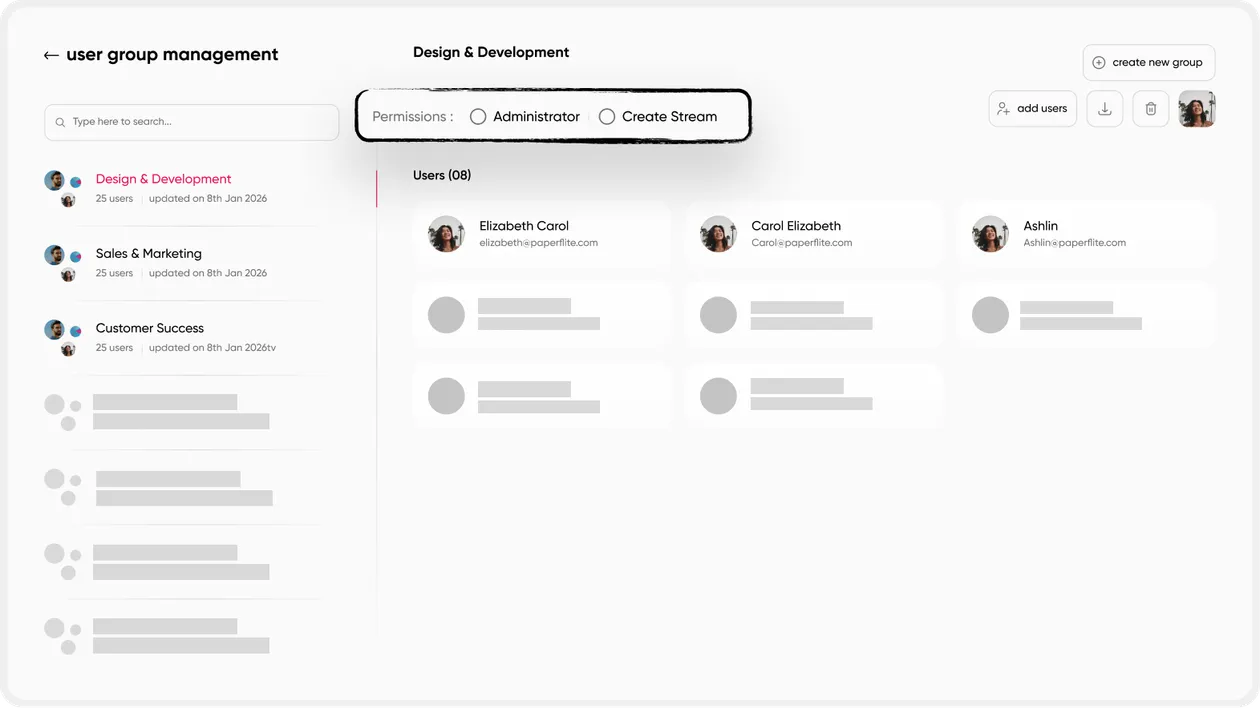
Managing user groups and their associated content permissions in one view.
Paperflite's Content Hub applies group-based permissions across sales stage, persona, and territory, so the setup above maps directly onto how the platform works rather than requiring a separate access-control layer bolted on top.
Streams and Collections let you build the role-specific kits from Step 4 without rebuilding a folder tree every time; a role gets its own curated view of the hub, and updating the underlying content updates every kit it appears in automatically. Seek, Paperflite's AI-powered search, is scoped to the same permissions, so the risk described in Step 5, search surfacing something a role shouldn't see, doesn't come up in the first place.
The Content Hub library overview, showing role-scoped categories at a glance.
If your team is still managing access with individual shares and a lot of institutional memory about who's allowed to see what, this is usually the point where it's worth seeing how it works in practice.
Conclusion
A role-based sales collateral library isn't a bigger folder structure. It's a system that keeps working the same way whether your sales team is ten people or two hundred, because access lives on the role instead of on someone's memory of who's supposed to see what. Map the roles, structure the hub around them, assign permissions to the group, package the collections, and keep search inside the same boundaries. Do those five things in order and the "wrong deck, wrong hands" problem from the top of this article stops being a recurring incident and starts being something your system prevents by default.
For the folder-and-tagging side of this same problem, 7 must-have features of content hub covers what else to look for beyond permissions.
FAQ
What is a role-based sales collateral library?
It's a content library where access is granted by job function or team instead of by individual user. Every AE, SDR, partner, or CS rep sees only the content mapped to their role, so nobody has to guess what's approved for them to use.
How is role-based access different from individual permissions?
Individual permissions are set person by person and break down as a team grows past a few dozen people. Role-based access assigns permissions to a group once, and every person in that role inherits it automatically, including new hires.
What roles should a sales content library actually have?
Most teams start with around six: AE, SDR, sales manager, partner or reseller, customer success, and admin. Add more only when a group genuinely needs a different content set than the roles around it, not for every job title on the org chart.
Does role-based access slow down content approval?
It usually speeds it up. Marketing sets permissions once per role instead of reviewing and approving individual access requests every time someone new joins a team.
Can partners and resellers use a role-based library too?
Yes. External roles like partner or reseller are set up the same way as internal ones, scoped to only the co-branded or partner-approved content, with everything else in the library staying out of view.
How often should role permissions be reviewed?
Quarterly is a reasonable default, or any time team structure changes significantly, a reorg, a new partner tier, or a product line getting sunset. Permissions drift out of sync with reality faster than most teams expect.
PAPERFLITE'S CONTENT TECHNOLOGY IN ACTION
IT'S EASIER THAN FALLING OFF A LOG
(DON'T ASK US HOW WE KNOW THAT)
Paperflite: role-based content hubs, sales kits, and AI search built for revenue teams.
Privacy Policy
Terms of Service
© 2026 Paperflite